The journal
Is there a password manager available for Microsoft Teams? A practical guide
password manager teams sharing explained, with practical workflows and a checklist to secure credential sharing in Microsoft Teams.
Quick answer and what 'password manager teams sharing' means
Short direct answer
Short answer: you can use a password manager alongside Microsoft Teams to share and manage credentials, but Teams itself is not a credential vault and most solutions surface links or controlled access rather than storing secrets inside chat.
Is there a password manager that supports secure sharing workflows with Microsoft Teams?
Yes. You can use a password manager alongside Microsoft Teams to share credentials safely, but integrations usually surface credentials or provide controlled links rather than storing secrets in Teams itself. Choose a manager that supports SSO, per-item permissions, audit logs and ephemeral link sharing to match your team needs.
Why this question matters for small teams
When teams search for password manager teams sharing they are usually asking whether they can give teammates secure access to shared accounts from inside the Teams workflow, without copying passwords into chat or leaving audit gaps.
For small teams this matters because shared credentials are often used across services, and sloppy sharing increases the chance of reuse, lost access and unclear ownership. Centralizing credentials in a manager gives clearer sharing rules, reduces password reuse and makes recovery and rotation more practical.
Common meanings behind the phrase include several patterns: a fully integrated Teams app that surfaces stored credentials, link-based or ephemeral shares posted into a Teams conversation, single sign-on or SSO-based account linking so team members authenticate with directory identities, or simply curated notes with connection details that teammates can access. Understanding which meaning applies affects how you evaluate any vendor or workflow.
How password managers can integrate with Microsoft Teams workflows
Integration patterns: bot, tabs, SSO and links
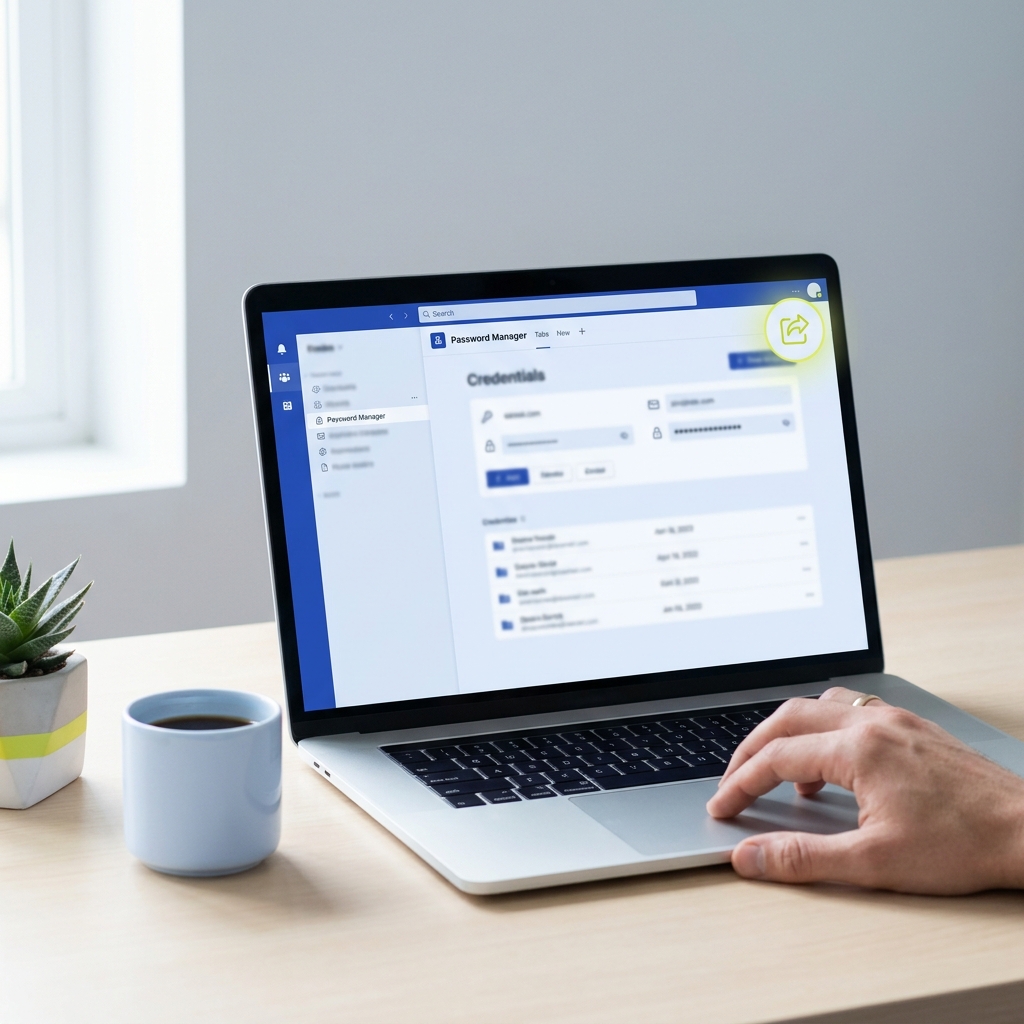
There are a few practical integration patterns you will see when someone asks about Teams password manager integration. A Teams app can add a tab that opens a vault interface, letting users view or request credentials without leaving Teams. Bots or message actions can surface a secure link or a one-time secret on request. Many teams use SSO or OAuth to connect a single identity to the password manager so users do not need a separate login. See our guidance on choosing and integrating tools in the software selection process: guides on choosing business software.
Look for a Teams app that supports secure link sharing and SSO
What integration does and does not do
Integrations are convenient but have technical boundaries. A Teams integration usually acts as a surface for credentials that remain stored in the password manager, or it posts controlled links that expire. Teams itself does not become the secure vault; it is the carrier for discovery, access requests and notifications.
Authentication for integrations commonly relies on OAuth or SSO with your corporate directory so access decisions align with directory group membership. That aligns with vendor discussions about access and password management in Teams: Microsoft Q&A. That means account provisioning and deprovisioning are typically handled at the identity layer, not inside Teams chat.
Keep expectations clear: integration reduces context switching and can place credential discovery in the chat flow, but it does not remove the need for strong access controls, audit logging and rotation policies within the password manager itself.
How to choose a password manager for Teams sharing
Decision criteria checklist
Use this checklist to evaluate solutions that claim support for password manager teams sharing: access controls and granularity for shared vaults or folders, per-user and per-item permissions, audit and activity logs with exportable records, SSO support for your directory, provisioning hooks or SCIM support, admin controls for recovery and emergency access, and client support for the devices your team uses.
Questions to ask vendors or IT stakeholders
When you speak to vendors or your internal IT team, ask clear questions: can the solution integrate with your identity provider for SSO and automatic deprovisioning, what granularity of sharing does it offer, does it produce readable audit trails, can you create ephemeral shared links, and how is MFA enforced for vault access?
Also weigh usability against security. For small teams a shared vault with simple role permissions can be faster to adopt, while ephemeral links or just-in-time access may be better for sensitive vendor accounts. Ensure the chosen pattern matches a practical onboarding and recovery approach for your team.
Step-by-step: common setup and sharing workflows for Teams
Basic setup for a small team
1. Choose a password manager that supports team or business plans and confirms SSO or OAuth compatibility with your directory. For practical guidance on secure sharing patterns see best practices.
2. Configure SSO so users sign in with team identities and enable MFA on the identity provider and the password manager accounts.
3. Create shared vaults or folders for common services and assign roles or permissions to users or groups; document who owns each vault and who can approve changes.
Examples of secure sharing workflows inside Teams
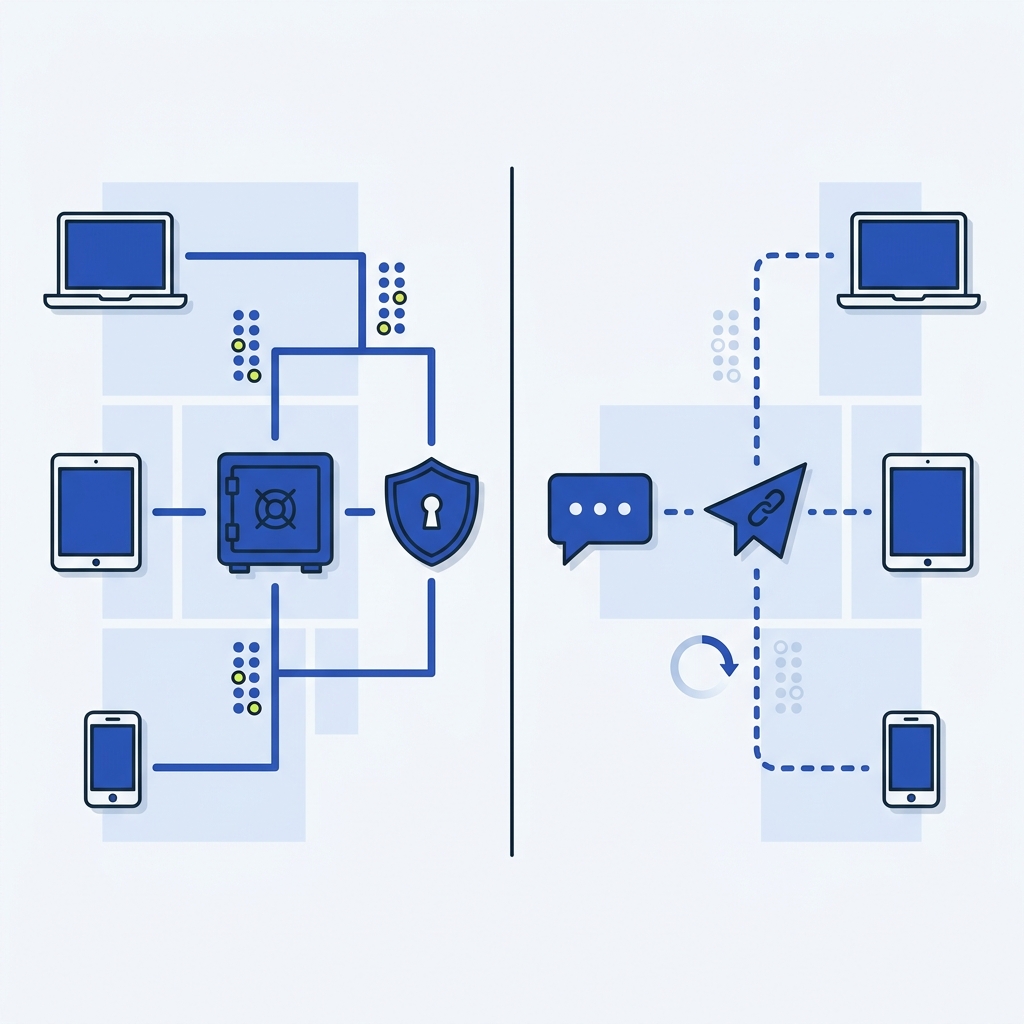
Example A, active collaboration: For ongoing projects create a shared vault for the project, grant team members the minimum role they need, and use the Teams app tab to link directly to the vault. When someone needs a password they open the vault and copy credentials through the manager tool rather than pasting into chat. Rotate credentials after role changes or leaving members.
Example B, ad-hoc vendor access: When an external vendor needs temporary access, generate an ephemeral link from the manager and post the link to a private Teams channel. Set an expiry and enable a retrieval audit so you can see who used the link. Revoke or rotate the credential after the work completes.
Operational tips: maintain an owner for each shared vault, enforce rotation schedules for high-risk accounts, and ensure recovery paths are in place in case the primary admin loses access. Use multi-factor authentication everywhere and regularly review membership in shared vaults.
Common mistakes and security pitfalls to avoid when sharing passwords via Teams
Frequent operational errors
Teams is built for conversation, so a typical mistake is copying credentials into a chat message. This leaves a long-lived, untracked copy of the secret. Another common error is over-broad sharing, where a folder is open to more people than necessary. Teams also makes it easy to forward messages, so consider that when deciding where to post sensitive links.
How to mitigate human risk
Mitigations are straightforward: use the password manager to share rather than chat, enforce least privilege for shared vaults, enable logging and alerts for unusual access patterns, and train teammates on the required workflow. Short, practical training and an accessible team policy reduce accidental risky behaviour more than long technical documents.
Escalate to IT or security if you detect untracked credential sharing, an account compromise, or if your chosen solution lacks required administrative controls. These are the moments when centralized access and clear auditing make a real difference.
Practical scenarios, sample policies and next steps
Sample short policy for small teams
Short policy example: Only approved team password manager tools may be used for sharing credentials. Do not paste passwords into Teams chat. Use shared vaults or ephemeral links for vendor access. Owners must rotate high-risk credentials every 90 days and immediately after a suspected compromise. All access to shared vaults must be logged.
When to consider scaling to enterprise controls
Use enterprise controls if you need tighter provisioning, SCIM automation for accounts, legal or compliance audits that require long-term exportable logs, or conditional access policies tied to device posture. For many small teams, a lightweight business plan with SSO and audit logs provides the necessary controls without heavy administration.
Next steps checklist: trial one manager with your core team, document the workflow in the team handbook, schedule a short training session, and review the arrangement after 30 days to confirm it fits daily operations.
Frequently asked questions
Can I store passwords inside Microsoft Teams?
No. Microsoft Teams is a collaboration platform, not a secure credential vault. Use a dedicated password manager and surface access through Teams integrations or links.
How do I give temporary access to an external vendor via Teams?
Generate an ephemeral link or create a temporary account in the password manager, share the link or credentials via a private channel, then revoke or rotate the credential when work is complete.
What are the minimal controls a small team should require?
Require SSO and MFA, role-based shared vaults, audit logging, and a documented rotation policy for high-risk credentials.
Start small, choose a single sharing pattern, and put it in your team handbook. Trial the workflow for 30 days, then review and tighten controls where needed. Clear ownership, enforced MFA, and routine rotation will reduce risk and make shared access easier to manage than ad-hoc chat exchanges.
References
- https://stackandmethod.com/guides/workflow-automation/
- https://stackandmethod.com/guides/choosing-business-software/
- https://stackandmethod.com/software/
- https://learn.microsoft.com/en-us/answers/questions/4402649/access-and-password-manager-in-teams
- https://1password.com/product/teams-small-business-password-manager
- https://bitwarden.com/blog/password-sharing-best-practices-for-teams/
- https://n8n.io/pricing/